About Me
I am a research fellow in Ilya Sergey’s Verse Lab at the National University of Singapore (NUS) and currently a visiting academic at the University of Cambridge with Tobias Grosser. I received my PhD from ETH Zurich in 2025, advised by Peter Müller, for my dissertation on the modular verification of security protocol implementations. During my PhD, I also spent two internships at Amazon Web Services (AWS), where I scaled my verification techniques to a production codebase of more than 100k lines of code.
Security protocols such as TLS, WireGuard, or Signal are only as secure as their implementations. My research develops techniques to prove, in a machine-checked way, that real-world protocol implementations satisfy security and privacy properties. To this end, I apply automated protocol verifiers such as Tamarin, auto-active program verifiers, and the Lean proof assistant to obtain guarantees that reach from an abstract protocol model all the way down to the code that is executed, and I scale these guarantees to large production codebases. I am also one of the lead maintainers of Gobra, an auto-active program verifier for the Go programming language.
Research
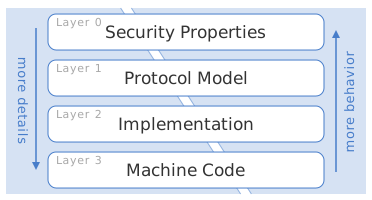
I design verification techniques and build the tools that apply them, spanning the entire stack from protocol models, to everyday programming languages, down to machine code.
A protocol model (layer 1) is a high-level abstraction of a protocol’s behavior, allowing us to focus on its security properties without being distracted by implementation details. Implementing a protocol in a programming language (layer 2) adds details such as data structures, concurrency, and the serialization of messages into their network representation. Compilers turn an implementation into machine code (layer 3), which is what computers execute.
For correctness, we need to ensure that the behavior permitted at each layer is less than or equal to the behavior permitted at the layer above, which is exactly what a refinement proof establishes.
Foundational Automation for Security Proofs
Tamarin is a state-of-the-art tool to prove security properties (layer 0) for protocol models (layer 1). Its high degree of automation made it possible to model and prove properties for drafts of protocol standards. However, Tamarin proves properties against a bespoke execution model.
In this project, we develop Tamalean, a framework embedded in the Lean proof assistant, which supports the same input language as Tamarin, thus, acting as a drop-in replacement for Tamarin. Tamalean states properties as Lean theorems against a simple execution model featuring a textbook attacker while retaining the level of automation known from Tamarin. All proofs are machine-checked by Lean and thus come with a minimal trusted computing base, namely Lean’s kernel. By being fully embedded in Lean, this project provides the foundation for other projects such as refining a protocol model to machine code.
Refinement Proofs down to Machine Code
Security properties (layer 0) proved for a protocol model (layer 1) carry over to an implementation (layer 2) only if the implementation behaves according to the model. To prove that this is the case, we generate I/O specifications from Tamarin models. These I/O specifications describe the permissible behavior of a protocol implementation, and we use off-the-shelf program verifiers to prove that an implementation satisfies its I/O specification.
This follow-up project establishes such refinement proofs in Lean: from a Tamalean model down to an implementation written in Lean. In collaboration with the Universities of Cambridge, Bristol, Lisbon, and Utah, we push these guarantees even further, through LLVM’s MLIR compiler all the way down to machine code (layer 3). The result is a single machine-checked proof of the protocol model’s properties for the compiled machine code.
Modular Proofs of Privacy Properties
Unlike many security properties, privacy properties such as anonymity, unlinkability, or vote privacy cannot be stated as properties of a single execution. They are indistinguishability properties: an attacker must not be able to tell two executions of a protocol apart. This project develops a methodology to prove indistinguishability properties modularly for protocol implementations (layer 2), extending my earlier invariant-based verification techniques beyond single-execution security properties.
Gobra
Gobra is a deductive, auto-active program verifier for the Go programming language, built on separation logic and the Viper verification infrastructure. It proves memory safety, crash safety, data-race freedom, and user-provided functional and security properties for real-world Go code (layer 2), and supports Go’s structural subtyping and channel-based concurrency.
Gobra IDE integrates Gobra into Visual Studio Code, verifying a program as it is edited and reporting errors inline. I am one of Gobra’s lead maintainers and use it for all my case studies, from the WireGuard VPN protocol to a 100k+ line production codebase.
Selected Publications
-
L. Arquint,“GCD: Garbled, Corrected, Demonstrandum – Fixing and Proving Go’s Extended GCD Implementation,” 2026 Workshop on Foundations of Computer Security (FCS), vol. abs/2606.05796, 2026.
[Abstract]
We verify the ’extendedGCD’ implementation in Go’s standard library (’crypto/internal/fips140/bigmod’), which plays a crucial role in the generation of RSA key pairs. Even though the Go implementation is supposedly a direct port from BoringSSL’s implementation, we uncovered two deviations that each break the algorithm’s invariants: (1) the Go implementation deviates in the way coefficients are updated, and (2) it permits a larger input domain. We address both deviations; the first by fixing the Go implementation, which results in an on average 24% speedup, and the second deviation by porting an existing proof for BoringSSL and extending it to cover the larger input domain. We prove correctness and termination of the fixed Go implementation using Gobra, a deductive program verifier for Go. Where necessary, we used Lean to prove key lemmata on non-linear arithmetic, which we import into Gobra. Our verification effort reveals three key insights: subtle bugs can slip into even well-reviewed code with surprising ease; formal verification is a powerful tool for uncovering them; and AI agents can facilitate the verification process by iteratively refining invariants and lemmata based on Gobra’s error messages.
[BibTeX]
@article{Arquint2026, author = {Arquint, Linard}, title = {GCD: Garbled, Corrected, Demonstrandum -- Fixing and Proving Go's Extended GCD Implementation}, booktitle = {2026 Workshop on Foundations of Computer Security (FCS)}, journal = {CoRR}, volume = {abs/2606.05796}, year = {2026}, doi = {10.48550/arXiv.2606.05796}, url = {https://doi.org/10.48550/arXiv.2606.05796}, urltext = {arXiv}, url1 = {https://www.linardarquint.com/assets/publications/Arquint2026.pdf}, url1text = {PDF} }[arXiv][PDF] -
L. Arquint, S. Kishor, J. R. Koenig, J. Dodds, D. Kroening, and P. Müller,“The Secrets Must Not Flow: Scaling Security Verification to Large Codebases,” in 2026 IEEE Symposium on Security and Privacy (S&P), 2026, pp. 1822–1841.
[Abstract]
Existing program verifiers can prove advanced properties about security protocol implementations, but are difficult to scale to large codebases because of the manual effort required. We develop a novel methodology called *Diodon* that addresses this challenge by splitting the codebase into the protocol implementation (the *Core*) and the remainder (the *Application*). This split allows us to apply powerful semi-automated verification techniques to the security-critical Core, while fully-automatic static analyses scale the verification to the entire codebase by ensuring that the Application cannot invalidate the security properties proved for the Core. The static analyses achieve that by proving *I/O independence*, i.e., that the I/O operations within the Application are independent of the Core’s security-relevant data (such as keys), and that the Application meets the Core’s requirements. We have proved Diodon sound by first showing that we can safely allow the Application to perform I/O independent of the security protocol, and second that manual verification and static analyses soundly compose. We evaluate Diodon on two case studies: an implementation of the signed Diffie-Hellman key exchange and a large (100k+ LoC) production Go codebase implementing a key exchange protocol for which we obtained secrecy and injective agreement guarantees by verifying a Core of about 1% of the code with the auto-active program verifier Gobra in less than three person months.
[BibTeX]
@inproceedings{ArquintKishorKoenigDoddsKroeningMueller26, author = {Arquint, Linard and Kishor, Samarth and Koenig, Jason R. and Dodds, Joey and Kroening, Daniel and M\"{u}ller, Peter}, title = {The Secrets Must Not Flow: Scaling Security Verification to Large Codebases}, booktitle = {2026 IEEE Symposium on Security and Privacy (S&P)}, year = {2026}, doi = {10.1109/SP63933.2026.00026}, pages = {1822-1841}, publisher = {IEEE}, url = {https://doi.org/10.1109/SP63933.2026.00026}, urltext = {Publisher}, url1 = {https://www.linardarquint.com/assets/publications/ArquintKishorKoenigDoddsKroeningMueller26.pdf}, url1text = {PDF}, url2 = {https://www.linardarquint.com/assets/publications/ArquintKishorKoenigDoddsKroeningMuellerExt25.pdf}, url2text = {extended version} }[PDF] -
L. Arquint,“Modular Verification of Security Protocol Implementations,” PhD thesis, ETH Zurich, 2025.
[Abstract]
Security protocols such as TLS or Signal ensure security and privacy for browsing the web, sending private messages, and using cloud services. It is, thus, crucial that these ubiquitous and critical protocols are designed *and* implemented correctly. Protocol model verifiers such as Tamarin and ProVerif make it viable to formally verify protocol *models*. However, proving protocol *models* secure is insufficient to guarantee secure *implementations*. Coding errors such as missing bounds checks (e.g., causing the Heartbleed bug), omitted protocol steps (as in the Matrix SDK), or ignored errors (e.g., returned by a TLS library) may invalidate all security properties proven for the corresponding models. This dissertation is centered around proving security properties in the symbolic model of cryptography for protocol *implementations*. This faces three key challenges. First, security properties like secrecy and authentication are *global properties*, which depend on the collective behavior of all protocol participants and the attacker. Accounting for this entire behavior in a proof presents a significant obstacle as implementation-level proof techniques rely heavily on local reasoning, which proves each method in isolation. Second, practically deployed protocol implementations are written in languages such as C, Go, Java or Rust and utilize *complex programming language features* like side effects, mutable state, and concurrency to achieve high performance. Despite complicating the reasoning about implementations and, thus, their security, it is crucial to support these features and programming languages to verify real-world protocol implementations. Third, protocol implementations are often embedded in *large software systems* to provide secure communication as a building block to application logic. Requiring a laborious proof for the entire software system is prohibitively expensive and, thus, impractical. This dissertation addresses all three key challenges. To address the first and second key challenge, this dissertation develops two novel verification methodologies. If an abstract model of a security protocol preexists, the first methodology exploits this abstract model to provide the required global view for proving security properties. In a second step, this methodology extracts proof obligations from the abstract model for implementations. Successfully discharging these proof obligations guarantees that an implementation refines an abstract model and, thus, inherits the security properties proven for the abstract model. The second methodology does not require a preexisting, accurate abstract model; instead, it uses invariants to establish a global view on the behavior of protocol participants and the attacker. By verifying each implementation against these invariants, we soundly consider the collective behavior in an implementation’s proof. Our evaluations on different security protocol implementations in C, Go, and Java demonstrate that both methodologies are applicable to a wide range of security protocols and programming languages. To address the third key challenge, this dissertation introduces *Diodon*, a novel and provably sound methodology to symbiotically combine proof systems of different expressive power, significantly reducing the proof effort and, thus, scaling security property verification to large, production codebases. We partition a codebase into its, typically small, security-critical part and the rest of the codebase for tailoring the employed proof system to each partition. Mandated by the security properties we want to prove, we apply a highly expressive but laborious program verifier to the security-critical part as we have to reason, e.g., about the content of messages and their cryptographic protection. We accomplish this task by using the aforementioned verification methodologies addressing the first and second key challenges and, thus, we directly benefit from their advances. Although the remaining partition is less security-critical, we cannot simply ignore it. A priori, there are ample opportunities for vulnerabilities in this partition because it is generally impossible to isolate the partitions for two main reasons. First, widely adopted programming languages like C, Go, and Java do not provide sufficiently strong isolation guarantees because such guarantees conflict with their features enabling high performance implementations like mutable state, aliasing, and concurrency. Second, refactoring a codebase to ensure - without relying on the programming language - that only the security-critical partition has access to sensitive data such as cryptographic keys can be prohibitively expensive and unacceptable from a performance perspective, as is the case for the production codebase on which we evaluate Diodon. Therefore, we apply lightweight, fully-automatic static analyses to ensure that the partitions soundly compose, i.e., without violating proven security properties. Our evaluation demonstrates that Diodon supports different coding styles and allows us to prove security properties for a production codebase of more than 100k LOC. In summary, this dissertation achieves sound and modular verification of security protocols implemented in real-world codebases, regardless of programming language, coding style or program verifier.
[BibTeX]
@phdthesis{Arquint2025, author = {Arquint, Linard}, title = {Modular Verification of Security Protocol Implementations}, school = {ETH Zurich}, year = {2025}, doi = {10.3929/ethz-c-000791717}, url = {https://www.linardarquint.com/assets/publications/Arquint2025.pdf}, urltext = {PDF} }[PDF] -
L. Arquint, M. Schwerhoff, V. Mehta, and P. Müller,“A Generic Methodology for the Modular Verification of Security Protocol Implementations,” in Computer and Communications Security (CCS), New York, NY, USA, 2023, pp. 1377–1391.
[Abstract]
Security protocols are essential building blocks of modern IT systems. Subtle flaws in their design or implementation may compromise the security of entire systems. It is, thus, important to prove the absence of such flaws through formal verification. Much existing work focuses on the verification of protocol *models*, which is not sufficient to show that their *implementations* are actually secure. Verification techniques for protocol implementations (e.g., via code generation or model extraction) typically impose severe restrictions on the used programming language and code design, which may lead to sub-optimal implementations. In this paper, we present a methodology for the modular verification of strong security properties directly on the level of the protocol implementations. Our methodology leverages state-of-the-art verification logics and tools to support a wide range of implementations and programming languages. We demonstrate its effectiveness by verifying memory safety and security of Go implementations of the Needham-Schroeder-Lowe, Diffie-Hellman key exchange, and WireGuard protocols, including forward secrecy and injective agreement for WireGuard. We also show that our methodology is agnostic to a particular language or program verifier with a prototype implementation for C.
[BibTeX]
@inproceedings{ArquintSchwerhoffMehtaMueller23, author = {Arquint, Linard and Schwerhoff, Malte and Mehta, Vaibhav and M\"uller, Peter}, title = {A Generic Methodology for the Modular Verification of Security Protocol Implementations}, year = {2023}, isbn = {9798400700507}, publisher = {Association for Computing Machinery}, address = {New York, NY, USA}, booktitle = {Computer and Communications Security (CCS)}, pages = {1377-1391}, numpages = {15}, keywords = {protocol implementation verification, symbolic security, separation logic, automated verification, injective agreement, forward secrecy}, location = {Copenhagen, Denmark}, series = {CCS '23}, doi = {10.1145/3576915.3623105}, url = {https://doi.org/10.1145/3576915.3623105}, urltext = {Publisher}, url1 = {https://www.linardarquint.com/assets/publications/ArquintSchwerhoffMehtaMueller23.pdf}, url1text = {PDF}, url2 = {https://www.linardarquint.com/assets/publications/ArquintSchwerhoffMehtaMuellerExt23.pdf}, url2text = {extended version}, url3 = {https://www.linardarquint.com/assets/publications/ArquintSchwerhoffMehtaMuellerAE23.pdf}, url3text = {Artifact Appendix} }[PDF] -
L. Arquint, F. A. Wolf, J. Lallemand, R. Sasse, C. Sprenger, S. N. Wiesner, D. Basin, and P. Müller,“Sound Verification of Security Protocols: From Design to Interoperable Implementations,” in 2023 IEEE Symposium on Security and Privacy (S&P), 2023, pp. 1077–1093.
[Abstract]
We provide a framework consisting of tools and metatheorems for the end-to-end verification of security protocols, which bridges the gap between automated protocol verification and code-level proofs. We automatically translate a Tamarin protocol model into a set of I/O specifications expressed in separation logic. Each such specification describes a protocol role’s intended I/O behavior against which the role’s implementation is then verified. Our soundness result guarantees that the verified implementation inherits all security (trace) properties proved for the Tamarin model. Our framework thus enables us to leverage the substantial body of prior verification work in Tamarin to verify new and existing implementations. The possibility to use any separation logic code verifier provides flexibility regarding the target language. To validate our approach and show that it scales to real-world protocols, we verify a substantial part of the official Go implementation of the WireGuard VPN key exchange protocol.
[BibTeX]
@inproceedings{ArquintWLSSWBM23, author = {Arquint, Linard and Wolf, Felix A. and Lallemand, Joseph and Sasse, Ralf and Sprenger, Christoph and Wiesner, Sven N. and Basin, David and M\"uller, Peter}, booktitle = {2023 IEEE Symposium on Security and Privacy (S&P)}, title = {Sound Verification of Security Protocols: From Design to Interoperable Implementations}, year = {2023}, volume = {}, number = {}, pages = {1077-1093}, keywords = {protocol-verification;symbolic-security;automated-verification;tamarin;separation-logic;implementation}, publisher = {IEEE}, month = may, doi = {10.1109/SP46215.2023.10179325}, url = {https://doi.org/10.1109/SP46215.2023.10179325}, urltext = {Publisher}, url1 = {https://www.linardarquint.com/assets/publications/ArquintWolfLallemandSasseSprengerWiesnerBasinMueller23.pdf}, url1text = {PDF}, url2 = {https://www.linardarquint.com/assets/publications/ArquintWolfLallemandSasseSprengerWiesnerBasinMueller22.pdf}, url2text = {extended version}, url3 = {https://youtu.be/65CcVWe2cE0}, url3text = {Talk} }[PDF][Talk] -
L. Arquint, P. Müller, W. Oortwijn, João. C. Pereira, and F. A. Wolf,“Code-Level Verification,” in The Complete Guide to SCION: From Design Principles to Formal Verification, Cham: Springer International Publishing, 2022, pp. 519–562.
[Abstract]
The verification effort described so far ensures that the SCION protocol guarantees the intended correctness and security properties. These design-level guarantees are essential, but by themselves do not guarantee that a SCION network actually works as intended. Errors in the protocol’s implementation could compromise its availability, correctness, or security—for instance, by causing a component to crash, skip essential checks, or leak confidential information. To guarantee the absence of errors in the SCION implementation, we employ code-level verification. Design-level and code-level verification complement each other and target different abstractions of the overall system. In particular, design-level verification provides specifications for many of the properties that need to hold for the implementation to be correct, for instance, the intended I/O behavior of each component. Other properties, such as memory safety, data-race freedom, and the absence of backdoors are specified directly on the code level.
[BibTeX]
@inbook{10.1007/978-3-031-05288-0_23, author = {Arquint, Linard and M{\"u}ller, Peter and Oortwijn, Wytse and Pereira, Jo{\~{a}}o. C. and Wolf, Felix A.}, title = {Code-Level Verification}, booktitle = {The Complete Guide to SCION: From Design Principles to Formal Verification}, year = {2022}, publisher = {Springer International Publishing}, address = {Cham}, pages = {519--562}, isbn = {978-3-031-05288-0}, doi = {10.1007/978-3-031-05288-0_23}, url = {https://doi.org/10.1007/978-3-031-05288-0_23}, urltext = {Publisher} } -
L. Arquint, D. Basin, T. Klenze, S. Liu, P. Müller, João. C. Pereira, C. Sprenger, and F. A. Wolf,“Current Status and Plans,” in The Complete Guide to SCION: From Design Principles to Formal Verification, Cham: Springer International Publishing, 2022, pp. 563–572.
[Abstract]
In the previous chapters we have motivated the need for formal methods—both at the design level and the code level—and discussed techniques for both levels. We have seen the results of verification efforts related to the SCION data plane and the N-Tube algorithm and discussed example code from the SCION border router.
[BibTeX]
@inbook{10.1007/978-3-031-05288-0_24, author = {Arquint, Linard and Basin, David and Klenze, Tobias and Liu, Si and M{\"u}ller, Peter and Pereira, Jo{\~{a}}o. C. and Sprenger, Christoph and Wolf, Felix A.}, title = {Current Status and Plans}, booktitle = {The Complete Guide to SCION: From Design Principles to Formal Verification}, year = {2022}, publisher = {Springer International Publishing}, address = {Cham}, pages = {563--572}, isbn = {978-3-031-05288-0}, doi = {10.1007/978-3-031-05288-0_24}, url = {https://doi.org/10.1007/978-3-031-05288-0_24}, urltext = {Publisher} } -
F. A. Wolf, L. Arquint, M. Clochard, W. Oortwijn, J. C. Pereira, and P. Müller,“Gobra: Modular Specification and Verification of Go Programs,” in Computer Aided Verification (CAV), 2021, vol. 12759, pp. 367–379.
[Abstract]
Go is an increasingly-popular systems programming language targeting, especially, concurrent and distributed systems. Go differentiates itself from other imperative languages by offering structural subtyping and lightweight concurrency through goroutines with message-passing communication. This combination of features poses interesting challenges for static verification, most prominently the combination of a mutable heap and advanced concurrency primitives. We present Gobra, a modular, deductive program verifier for Go that proves memory safety, crash safety, data-race freedom, and user-provided specifications. Gobra is based on separation logic and supports a large subset of Go. Its implementation translates an annotated Go program into the Viper intermediate verification language and uses an existing SMT-based verification backend to compute and discharge proof obligations.
[BibTeX]
@inproceedings{WolfArquintClochardOortwijnPereiraMueller21, author = {Wolf, Felix A. and Arquint, Linard and Clochard, Martin and Oortwijn, Wytse and Pereira, Jo{\~{a}}o C. and M{\"u}ller, Peter}, title = {{G}obra: Modular Specification and Verification of Go Programs}, booktitle = {Computer Aided Verification (CAV)}, editor = {Silva, Alexandra and Leino, K. Rustan M.}, series = {LNCS}, volume = {12759}, publisher = {Springer International Publishing}, pages = {367--379}, year = {2021}, doi = {10.1007/978-3-030-81685-8_17}, url = {https://link.springer.com/chapter/10.1007/978-3-030-81685-8_17}, urltext = {Publisher}, url1 = {https://www.linardarquint.com/assets/publications/WolfArquintClochardOortwijnPereiraMueller21.pdf}, url1text = {PDF}, url2 = {https://ucl-pplv.github.io/CAV21/poster_P_186/#tab-extended}, url2text = {Talk} }[PDF][Talk] -
L. Arquint,“Profiling Symbolic Execution,” Master Thesis, ETH Zurich, Zurich, 2019.
[BibTeX]
@mastersthesis{20.500.11850/392350, copyright = {In Copyright - Non-Commercial Use Permitted}, year = {2019}, type = {Master Thesis}, author = {Arquint, Linard}, size = {95 p.}, language = {en}, address = {Zurich}, publisher = {ETH Zurich}, doi = {10.3929/ethz-b-000392350}, title = {Profiling Symbolic Execution}, school = {ETH Zurich}, url = {https://doi.org/10.3929/ethz-b-000392350}, urltext = {Research Collection} } -
S. Schmid, L. Arquint, and T. R. Gross,“Using Smartphones as Continuous Receivers in a Visible Light Communication System,” in Proceedings of the 3rd Workshop on Visible Light Communication Systems, New York, NY, USA, 2016, pp. 61–66.
[Abstract]
Visible Light Communication (VLC) allows to reuse a lighting infrastructure for communication while its main purpose of illumination can be carried out at the same time. Light sources based on Light Emitting Diodes (LEDs) are attractive as they are inexpensive, ubiquitous, and allow rapid modulation. This paper describes how to integrate smartphones into such a communication system that supports networking for a wide range of devices, such as toys with single LEDs as transmitter and receivers as well as interconnected LED light bulbs. The main challenge is how to employ the smartphone without any (hardware) modification as a receiver, using the integrated camera as a (slow) light sampling device. This paper presents a simple software-based solution, exploiting the rolling shutter effect and slow motion video capturing capabilities of latest smartphones to enable continuous reception and real-time integration into an existing VLC system. Evaluation results demonstrate a working prototype and report communication distances up to 3m and a maximum data throughput of more than 1200b/s, improving upon previous work.
[BibTeX]
@inproceedings{10.1145/2981548.2981558,
  author = {Schmid, Stefan and Arquint, Linard and Gross, Thomas R.},
  title = {Using Smartphones as Continuous Receivers in a Visible Light Communication System},
  year = {2016},
  isbn = {9781450342537},
  publisher = {Association for Computing Machinery},
  address = {New York, NY, USA},
  booktitle = {Proceedings of the 3rd Workshop on Visible Light Communication Systems},
  pages = {61-66},
  numpages = {6},
  keywords = {rolling shutter effect, visible light communication, free-space optics, communication protocols},
  location = {New York City, New York},
  series = {VLCS '16},
  doi = {10.1145/2981548.2981558},
  url = {https://doi.org/10.1145/2981548.2981558},
  urltext = {Publisher}
}
Awards
- 2025
-
2024
Amazon Inventor, U.S. Patent Application No. 18/901,581 A Method for Extending Safety Proofs of Protocols to Industrial Applications(with Samarth Kishor, Jason Koenig, and Joey Dodds)
-
2023
Innovative Tool Feature Award, VerifyThis 2023, for first-class predicates in Gobra(with João C. Pereira)
-
2012
Best High School Graduate, Gymnasium & Internat Kloster Disentis
Talks
-
Jul 2026
GCD: Garbled, Corrected, Demonstrandum – Fixing and Proving Go’s Extended GCD Implementation· [Slides]Workshop talk at FCS 2026, Lisbon
-
May 2026
Scaling Verification of Security Protocol Implementations: A Symbiotic Combination of Program Verification & Static AnalysesInvited talk at Carnegie Mellon University, PittsburghInvited talk at Programming Languages Seminar, National University of Singapore
-
May 2026
The Secrets Must Not Flow: Scaling Security Verification to Large CodebasesConference talk at S&P 2026, San Francisco
- Nov 2025
-
Apr 2025
Verification of Security Protocol Implementations· [Slides]Invited talk at National University of Singapore
-
Sep 2024
Refinement-Based Verification of Security Protocol Implementations· [Slides]Workshop talk at AWS FReE Workshop, Boston
-
Jan 2024
Using Separation Logic for Proving Security Protocol Implementations Secure· [Slides]Workshop talk at Swiss Verification Day, Neuchâtel
-
Nov 2023
A Generic Methodology for the Modular Verification of Security Protocol ImplementationsConference talk at CCS 2023, Copenhagen
-
May 2023
Sound Verification of Security Protocols: From Design to Interoperable Implementations· [Recording]Conference talk at S&P 2023, San Francisco
-
Jun 2022
Code-Level Protocol VerificationInvited talk at Zurich Information Security & Privacy Center (ZISC) Seminar, Zurich
-
Jul 2021
Gobra: Modular Specification and Verification of Go Programs· [Recording]Conference talk at CAV 2021, online
Student Supervision
-
PhD
Yueyang Feng · Security Protocol Refinements in Lean(officially supervised by Ilya Sergey)
-
Internship
Marwan Azizi · Automating Indistinguishability Proofs for Security Protocols
-
PhD
Valentin Mikhalchuk · Automating Implicit Dynamic Frames in Lean(officially supervised by Ilya Sergey)
-
PhD
Yuxi Ling · A Non-Interference Framework for Agentic Code(officially supervised by Ilya Sergey)
-
PhD
Vitaly Kurin · Verified Cost Bounds for Effectful Lean Programs(officially supervised by Ilya Sergey)
-
MSc
Kwok Wai Lui · Formal Verification of a Key Transparency Protocol· [Report](co-supervised with Felix Linker)
-
Practical Work
Cory Francis Myers · Formal Verification of a Key Transparency Protocol(co-supervised with Felix Linker)
-
MSc
Andrew Lee · A Temporal Program Logic for Data Protection· [Report](co-supervised with François Hublet)
- Practical Work
-
MSc
Lasse Meinen · Verification² of the Authentic Digital EMblem· [Report](co-supervised with Felix Linker)
- MSc
-
BSc
Dina Weiersmüller · Advanced Logical Proofs in a Verifier· [Report](co-supervised with Thibault Dardinier)
-
Research Fellowship
Vaibhav Mehta · A Generic Methodology for the Modular Verification of Security Protocol Implementations in C
-
BSc
Johannes Gasser · Program Verification in Continuous Integration Workflows· [Report](co-supervised with João C. Pereira)
- BSc
- BSc
- BSc
- BSc
-
MSc
Eva Charlotte Mayer · Assertion-based Testing of Go Programs· [Report](co-supervised with Felix A. Wolf)
- BSc
Academic Service & Teaching
-
Program committees
OOPSLA 2027, CSF 2027
-
Artifact evaluation
USENIX Security 2025 (Distinguished Artifact Reviewer)
-
Department service
VMI, Association of Scientific Staff of the Department of Computer Science at ETH Zurich: Vice-President (2022–2024), Executive Board Member (2021–2024), Department Conference Delegate (2020–2024), Studies Committee Delegate (2021).
VIS, Association of Computer Science Students at ETH Zurich: Member of the Higher Education Policy Commission (2016–2021), Department Conference Delegate (2016–2020).
-
Teaching
Head Teaching Assistant for the course Computer Science for electrical and mechanical engineering students at ETH Zurich in the spring semesters 2020, 2021, and 2022. The course teaches C++ and first concepts of computer science to over 850 students; I taught myself, supported and supervised about 35 teaching assistants each semester, prepared the weekly exercises on our online coding platform, and co-organized the computer-based exam.